Contents
- The caricature AI trend shows shadow AI has moved from personal habit to organizational risk
- Two things are exposed at once: work prompts and professional identity — what control does that affect
- Prompt control, approved instances, and history access: three gates that determine risk cost
- In Vietnam, shadow AI will surface most clearly in marketing, sales, and content teams
- What must be done so AI does not become a vulnerability: block prompts, block accounts, block habits
- References
The AI caricature trend may look like nothing more than a playful internet fad, but for marketers and operations teams in Vietnam, it is a very clear example of how a personal AI habit can touch business data. When users publicly share results created by ChatGPT, they also inadvertently reveal how they are using LLMs for work, how dependent they are on the tool, and even the possibility that they are putting sensitive information into a system outside internal control.
The key point is not the image itself, but the signal behind it: shadow AI, prompt leakage, and a target list for social engineering attacks. Analysis from TechRepublic shows that this is not only a privacy story, but also a corporate AI governance story, especially for marketing teams that are used to adopting AI tools quickly but have not yet put proper guardrails in place.
Key points
- The AI caricature trend can unintentionally confirm that employees are using LLMs for work-related tasks.
- If a public version not approved by the company is used, prompts may contain sensitive data and sit outside control.
- People who post publicly also create their own “target list” for phishing and social engineering.
- For Vietnamese marketers, the issue is process and review, not banning AI on instinct.
The caricature AI trend shows shadow AI has moved from personal habit to organizational risk
TechRepublic describes a trend spreading across Instagram and LinkedIn: users enter prompts for ChatGPT to create caricatures based on information about themselves and their jobs, then share the results publicly. On the surface, it is light, viral content. But in a corporate environment, this behavior shows that employees may be using LLMs to handle things related to their role, projects, or work context.
Josh Davies of Fortra, quoted in the original article, stresses that the bigger issue is that users are “talking to the LLM about work.” If they are not using a company-approved instance, they may already have put sensitive information into a public service. This is the gray zone of shadow AI: the tool is widely used, but security and governance teams cannot see it.
OWASP LLM Top Ten also lists Sensitive Information Disclosure as one of the top LLM risks. Put more plainly, the danger does not only come from AI giving the wrong answer, but from users accidentally turning prompts into a place where the company no longer controls the data.
Two things are exposed at once: work prompts and professional identity — what control does that affect
This trend does not only show that employees are using AI; it also shows that they are publicly describing their profession, position, and work context. TechRepublic gives examples of caricature images that clearly show roles such as banker, engineer, HR manager, developer, or healthcare provider. The title itself may not be a secret, but when it is paired with the confirmation “I use an LLM for this work,” the risk picture changes completely.
Prompt history: why an LLM account can become a reverse data vault
Davies notes that if an attacker takes over an LLM account, they may be able to view prompt history and find sensitive information that was previously entered. This is the most worrying point for marketing teams, because in practice prompts often contain briefs, campaign ideas, customer information, content scripts, or internal data to help the AI write faster. When a personal account is exposed, the entire “path” of the idea can be read back.
Source link: TechRepublic: Viral AI Caricatures Highlight Shadow AI Dangers
Public target lists: why social engineering gets easier when users label themselves
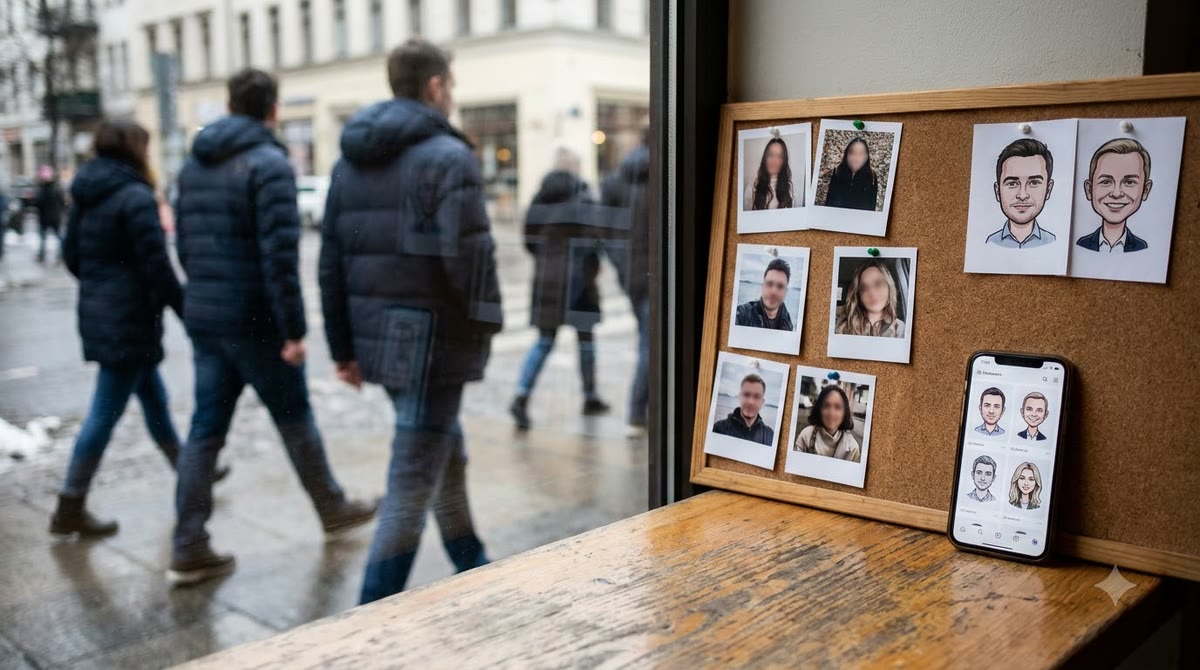
Publicly posting AI-generated images gives bad actors a large dataset to narrow down users who are likely using LLMs for work. From an attack perspective, this is a very useful source of phishing intelligence: know the job, know the platform being used, know how that person talks about themselves. For marketers, this shifts the story from “sharing for fun” to “handing attackers clues.”
Source link: TechRepublic: Viral AI Caricatures Highlight Shadow AI Dangers
Prompt control, approved instances, and history access: three gates that determine risk cost
Viewed from an operational mechanism, this trend raises three things that must be handled at the same time. First, control where employees are allowed to use AI. Second, limit what data can be entered into prompts. Third, know who has access to the conversation history with the tool. This is no longer about “whether to allow AI,” but about designing a process so AI does not outrun governance.
One often overlooked point is that the cost of shadow AI does not usually show up immediately in the budget. It appears as information risk, brand risk, and security risk. For marketing, just one person using a public LLM to work with sensitive content can affect the whole team if data leaks or the account is compromised.
That is why AI governance needs to move from vague recommendations to more concrete steps: define which tools are allowed, which data is forbidden in prompts, and who reviews AI use within the team. Without those three gates, the company is almost blind to what employees are doing with AI every day.
In Vietnam, shadow AI will surface most clearly in marketing, sales, and content teams
In Vietnam, this risk does not usually begin with highly complex systems, but with very ordinary habits: using a personal account to write proposals, summarize briefs, build outlines, translate content, or generate ideas for social posts. Because marketing work demands speed, teams are even more likely to “borrow” outside AI tools before they can get access to official systems.
That creates a very clear governance gap. Many Vietnamese companies have talked about digital transformation, but have not yet defined the boundary between approved tools and ad hoc tools. When staff use AI in their own way, data can leave before IT or security knows what happened. For agencies, the risk is even greater because one account can touch multiple clients at once.
For Vietnamese marketers, the practical conclusion is: do not only ask what AI can do, ask who is allowed to use it, with what data, and who is responsible if a prompt becomes a leak point.
What must be done so AI does not become a vulnerability: block prompts, block accounts, block habits
- Allow staff to use only company-approved AI instances, especially for briefs, customer data, and internal documents.
- Write clear rules on which data must not be entered into prompts, even when testing ideas or drafting.
- Check how the team stores and shares LLM accounts; do not let one personal account hold too much work information.
- Include shadow AI in the security checklist and regular training for marketing, sales, CS, and agency partners.
In short, the AI caricature trend is not harmless entertainment. It is a visible signal of how shadow AI is slipping into everyday work, and also a reminder that any company that wants to use AI safely must control prompts, accounts, and habits before thinking about scale.
See more marketing analysis and guides at https://marketing365.vn.
Follow more analysis from Marketing365 to stay updated on the latest marketing trends.
Read more articles in the Digital Trends category.